
A serious flaw in Telegram Desktop versions up to 7.2.8 could let an attacker steal files accessible to the logged-in user after a malicious link was opened. The researcher's report identifies it as CVE-2026-107181 and confirms testing on Windows.
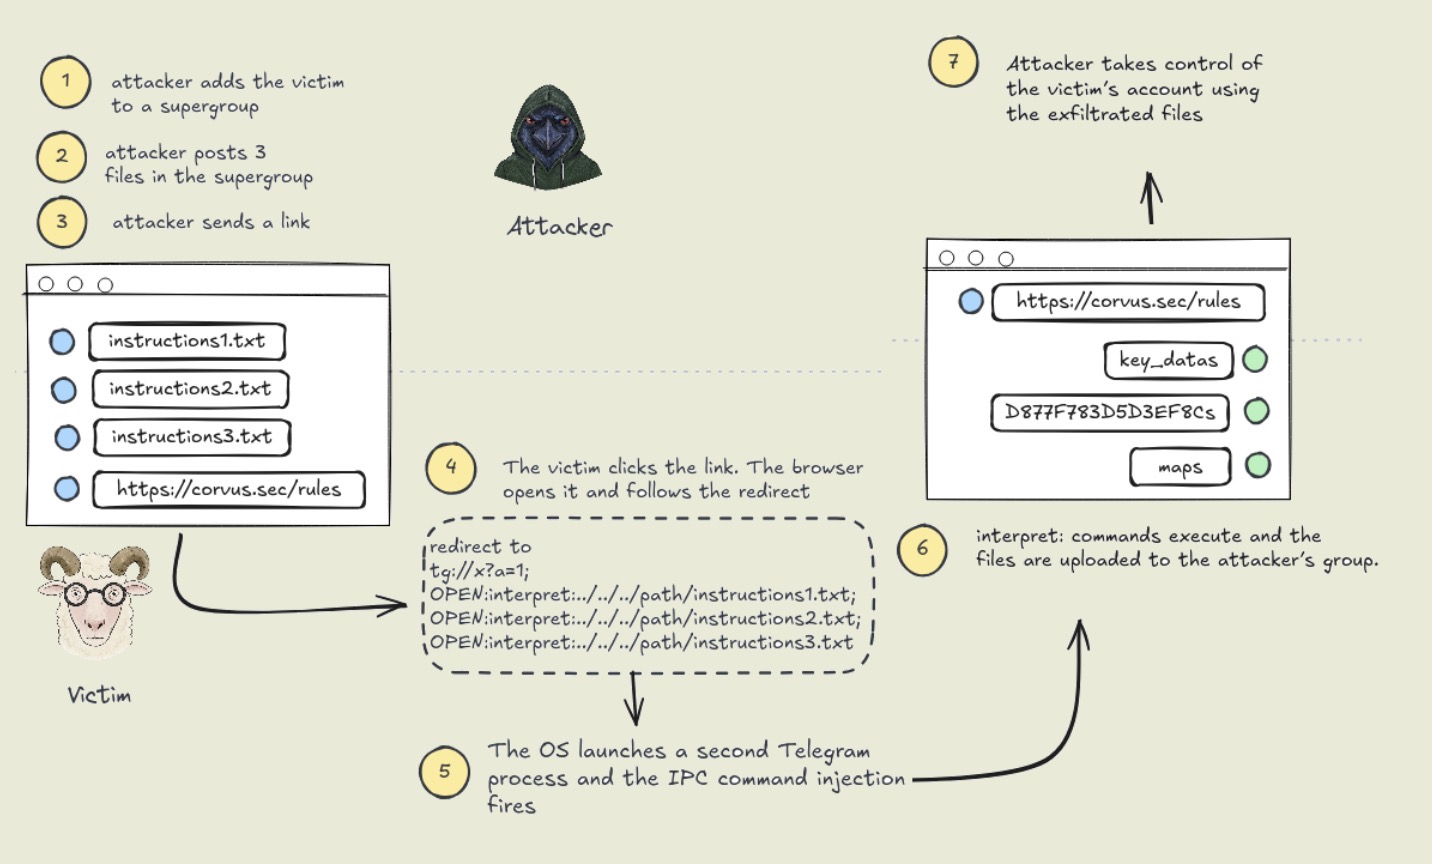
How a link could expose files
The problem involved Telegram's communication between desktop processes and a legacy internal file-sending feature. A crafted link could trigger an upload to an attacker-controlled chat without a file-send confirmation. Documents, exported chats, or locally stored wallet files could therefore be at risk; stolen Telegram session files could also enable account takeover under the conditions described in the report.
There is an important detail: the reported delivery route passes through the system browser, potentially after a redirect from an ordinary web link. It should not be described as every tg:// link clicked directly inside a Telegram chat automatically triggering the attack.
Update the desktop client
The fix is included in Telegram Desktop 7.2.9, not only in 7.3.0. Install the latest official release from Telegram Desktop. Users of third-party desktop clients should check whether their build includes the upstream fix; switching to an updated official client is an option if that is unclear.
Additional precautions include limiting group invitations, confirming download locations, and using a strong local passcode. These reduce exposure; installing the fixed client addresses the vulnerability.
Translated and fact-checked from the original Chinese article, dated October 9, 2026. Details checked against the researcher's disclosure, the upstream fix, and the 7.2.9 release. The Chinese article also links to OpenNET's report.
Comments NOTHING